The problem
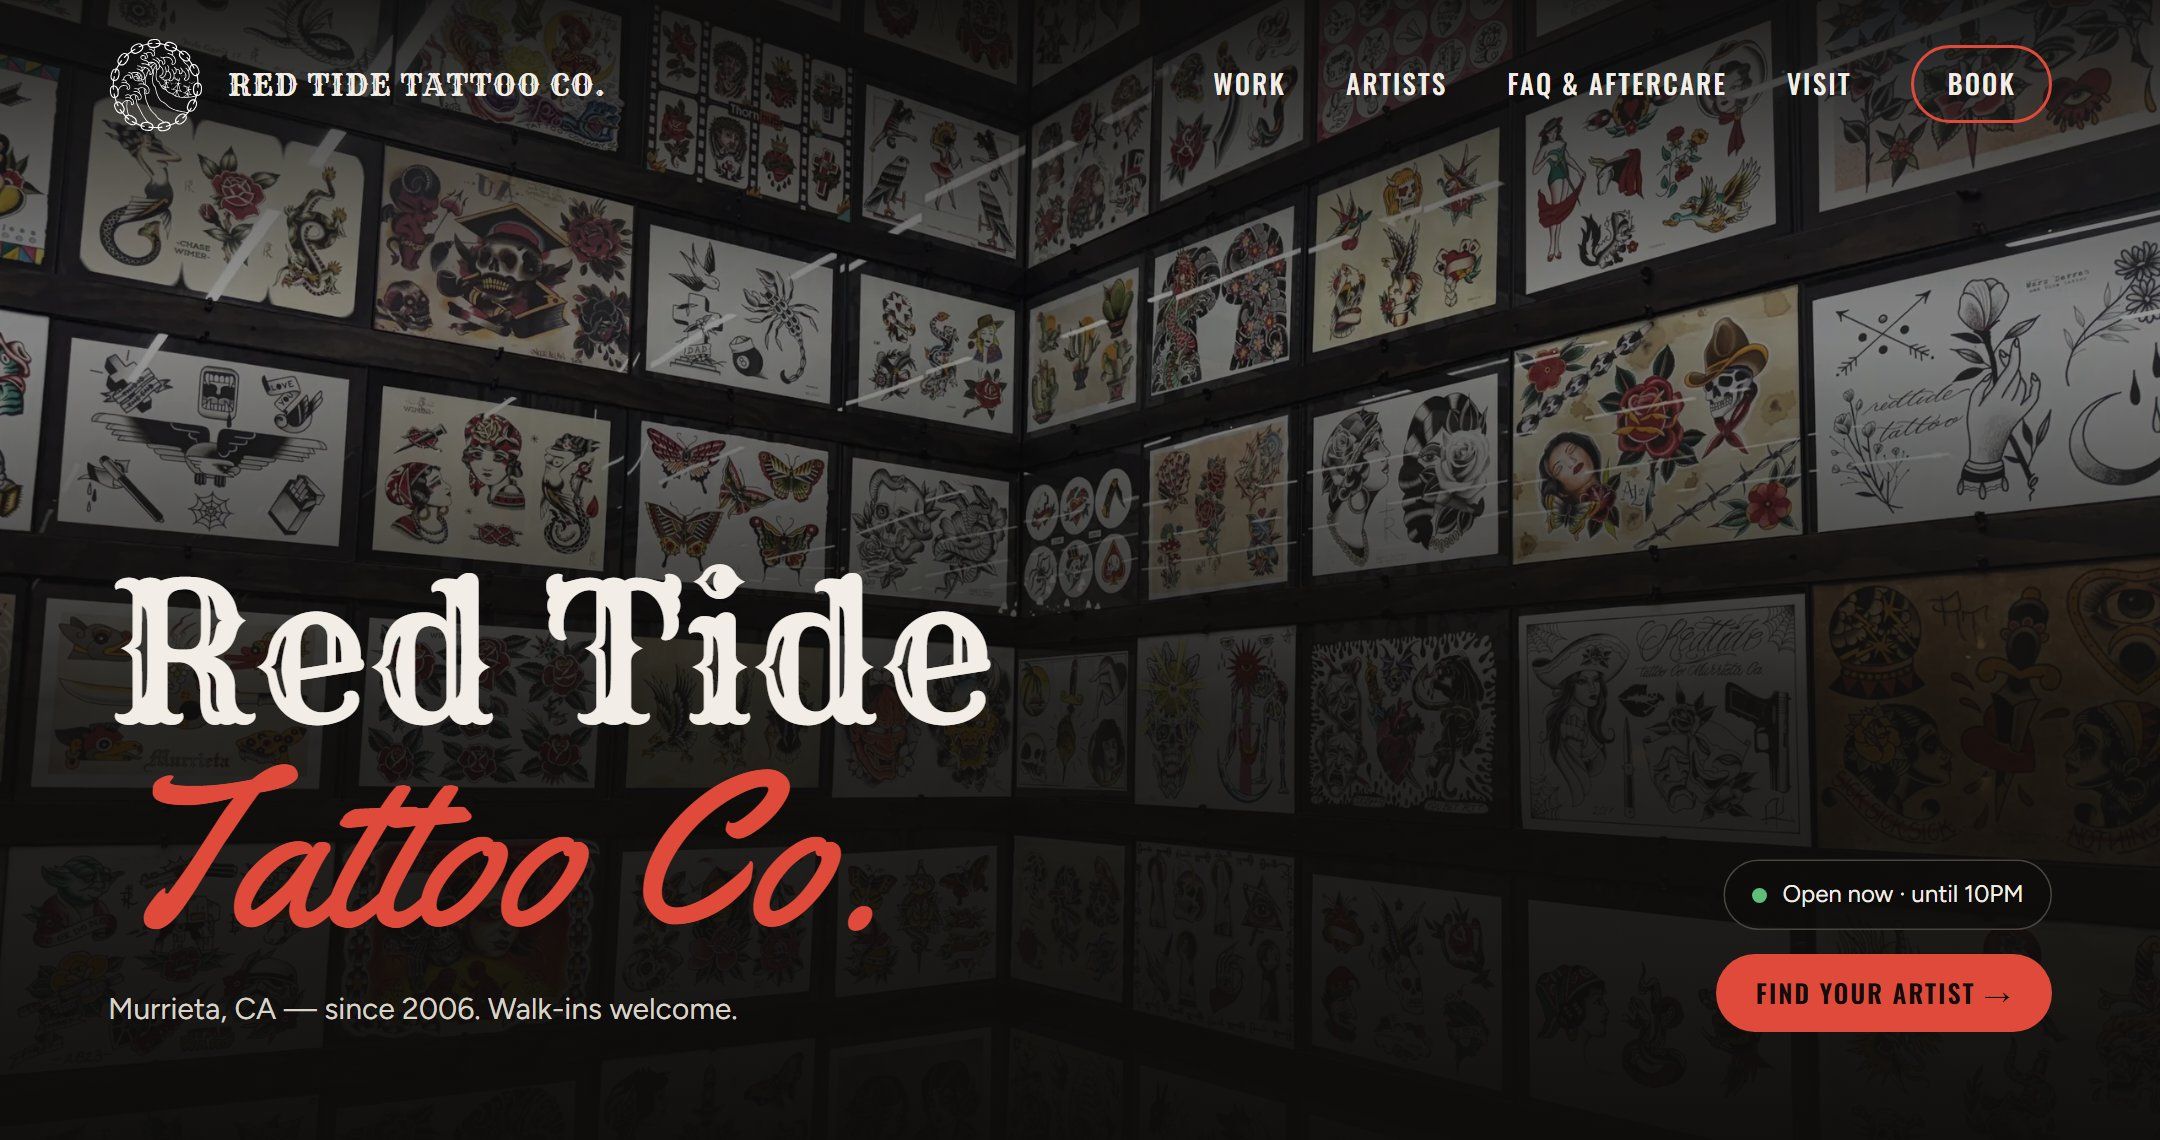
Red Tide Tattoo Co. has been tattooing in Murrieta, California since 2006. Its website ran on a paid WordPress.com Business plan, and the parts that mattered most to the shop were its consent forms: clients fill them in on their phones at the counter by scanning QR codes printed in the studio, so those addresses could not change.
My role
I did everything end to end: the design, the front end, the server code for the forms and the Instagram feed, moving the domain’s DNS to Cloudflare without disrupting the shop’s existing email, and setting up email delivery for the forms. I also wrote a plain-language guide so the owner can update artists, hours, holiday closures and FAQ text without me.
Approach
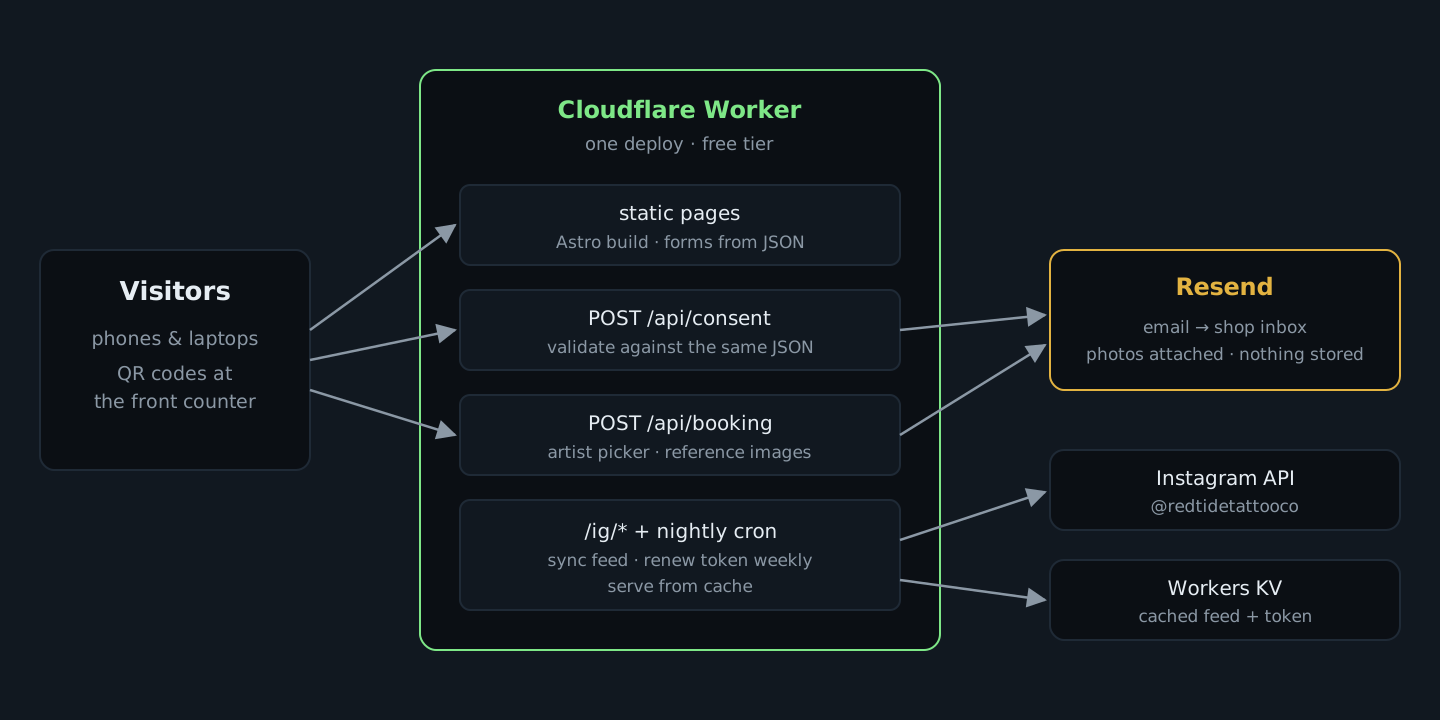
The site is a static Astro build served by a single Cloudflare Worker, which only runs code for the three things that need a server: consent forms, appointment requests and the Instagram feed.
- Consent forms. Tattoo, piercing and minor consent forms, each defined in one JSON file. The same file renders the form and validates the submission on the server, so the questions and the checks can’t drift apart. Submissions, including photos of the client’s ID, are emailed to the shop and never stored.
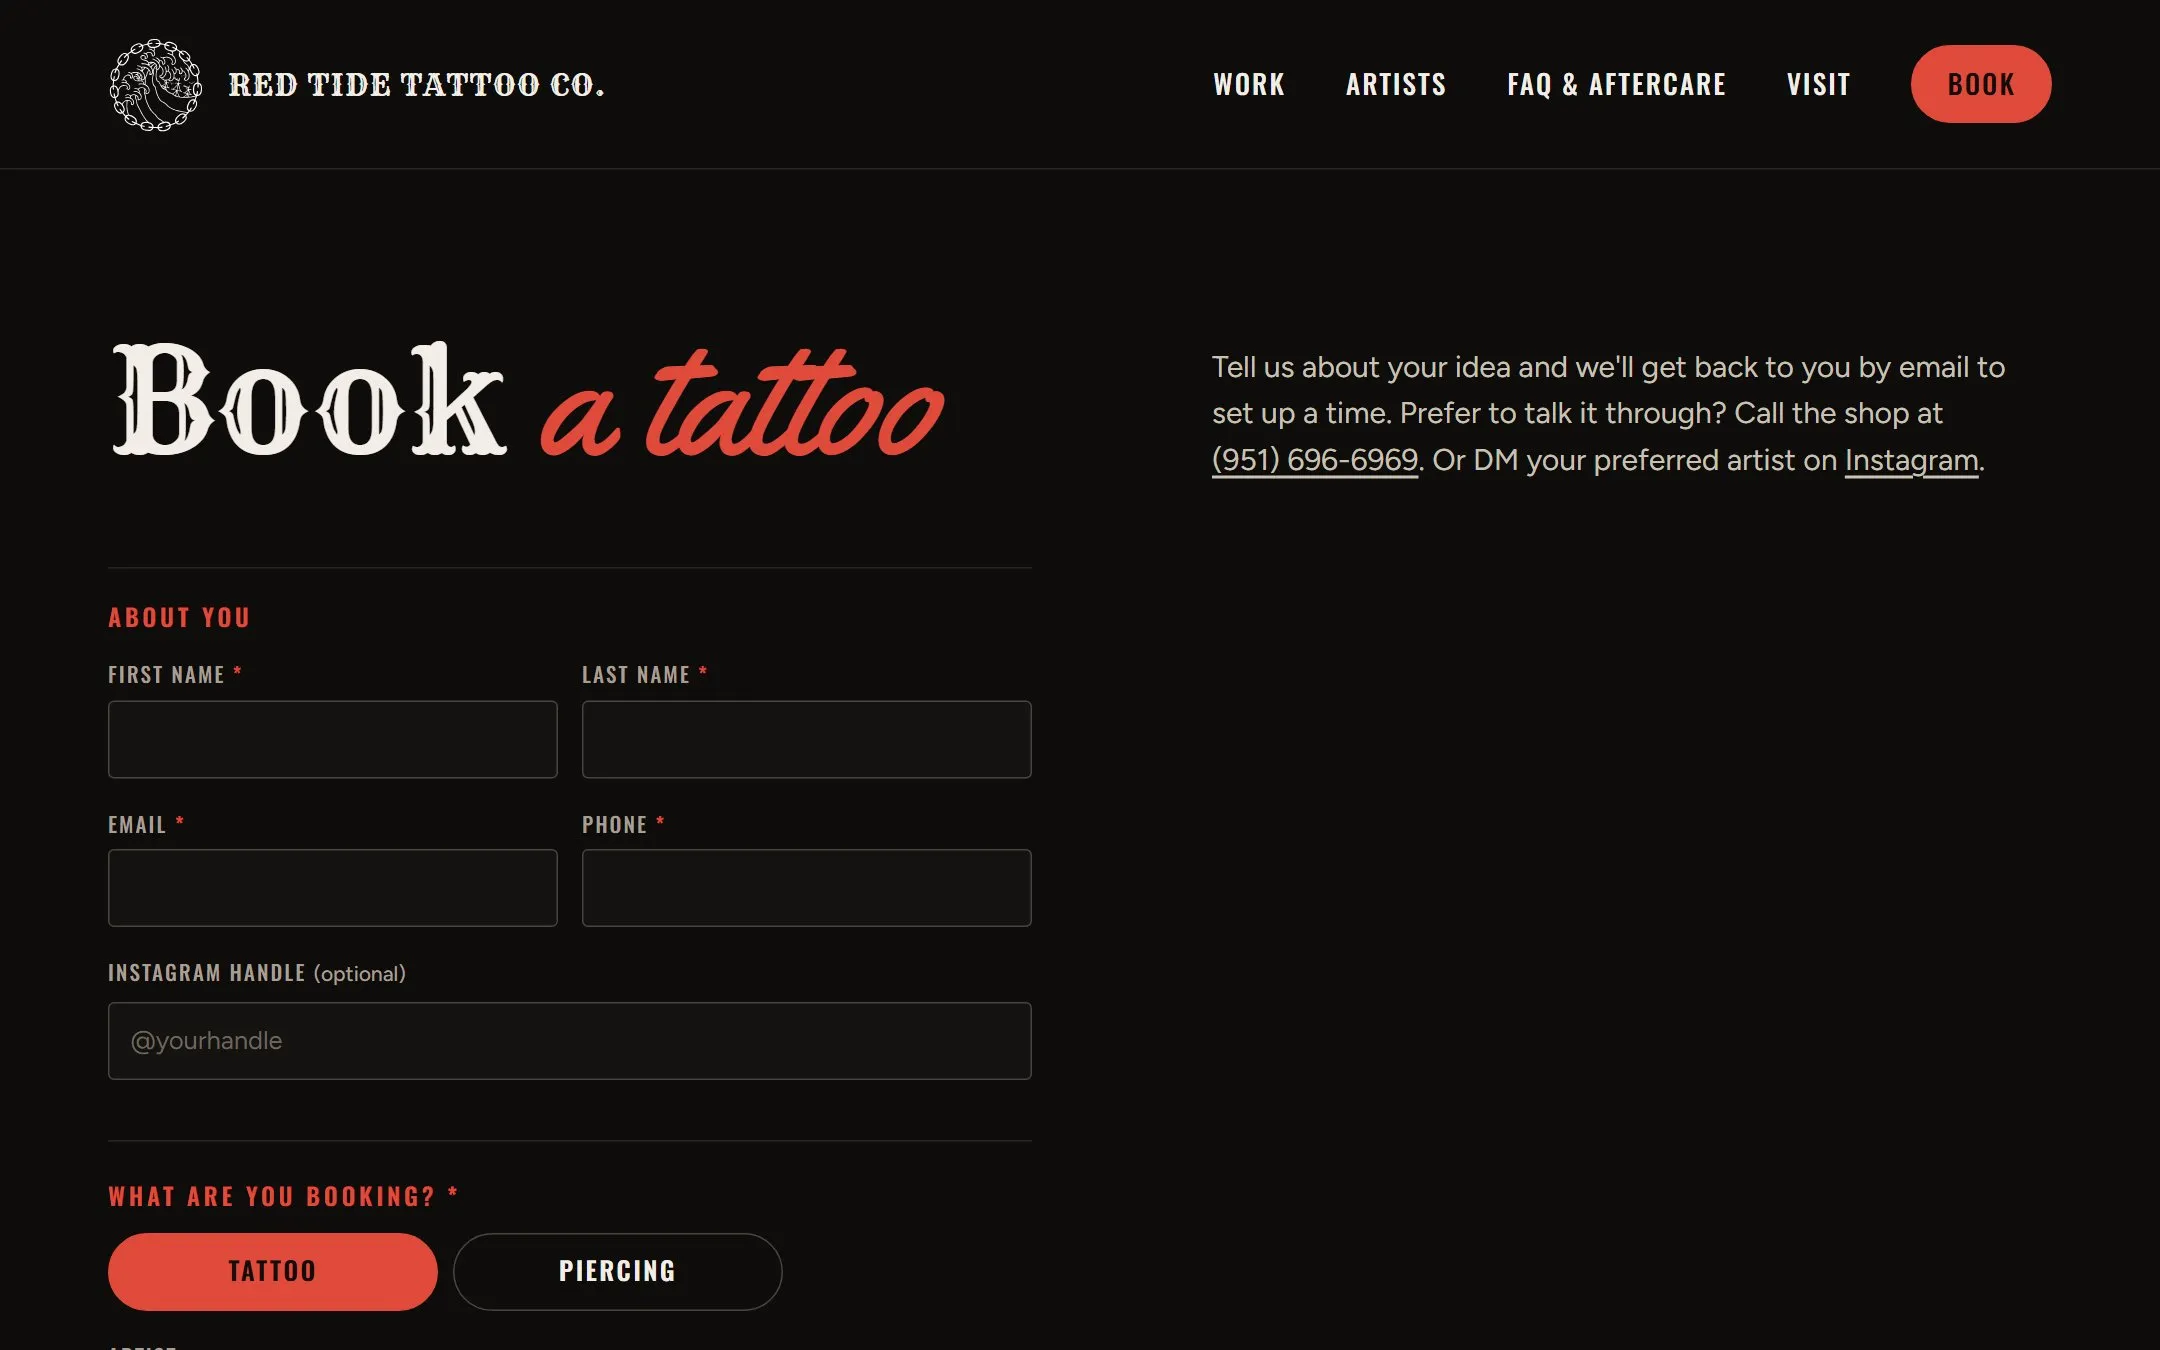
- Appointment requests. Clients choose tattoo or piercing, pick an artist or the piercer, describe their idea and attach up to five reference images. Each artist can share a link that pre-selects them, and the shop replies straight from the email.
- Instagram feed. A nightly job pulls the shop’s latest posts into a cache and renews the access token every week, so the page never waits on Instagram.
- Nothing breaks on launch day. Every old address, including the ones on printed QR codes, either still works or redirects to its new page.
Key decisions
- Email submissions instead of storing them
Consent forms include medical answers and ID photos. Sending them straight to the shop’s inbox means there’s no database of sensitive data to secure. The trade-off: no dashboard, so the inbox is the record.
- One JSON file per form, used by both the page and the server
Waiver wording and questions live in a single file the owner can review, and the server validates against that same file. The cost: a small custom form renderer instead of an off-the-shelf form service.
- Send form email from a separate subdomain
Form emails come from
mail.redtidetattooco.com, so their reputation is kept separate from the shop’s owninfo@mailbox. It took a few extra DNS records. - Cache Instagram nightly instead of embedding it
The feed loads from the site’s own cache, with no third-party embed scripts or trackers. Posts can be up to a day late, which is fine for a portfolio feed.
Results
The site launched on the shop’s domain on October 10, 2026, a week after the first commit. The old QR codes kept working, and the paid WordPress plan was left to expire: hosting now runs on free tiers. On a mobile Lighthouse audit of the live site, the home page scores 94 for performance and 100 for accessibility, best practices and SEO, and the booking page scores 97 for performance.
Stack & links
- --astro
- --cloudflare-workers
- --javascript
- --resend
- --instagram-api